Looking for the latest information on Deobfuscate Malicious Macro? We've compiled comprehensive data, records, and insights about Deobfuscate Malicious Macro.
Key Details
Explore the main sources for Deobfuscate Malicious Macro.
Developments
Stay updated on Deobfuscate Malicious Macro's latest milestones.
Creating a Malicious Macro – Learn How Hackers Trick You | Digital Defenders
Data is compiled from public records and verified media reports.
Last Updated: September 22, 2026
Final Thoughts
For 2026, Deobfuscate Malicious Macro remains one of the most talked-about information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
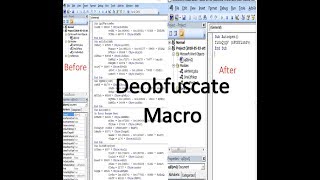
We will concentrate on macro embedded in Emotet downloader office document and see how to Article: ringzerolabs.com/2020/10/ Performing simple text transformations is often enough to This video is for educational purposes only. In this video, I demonstrate how attackers use Here I show how to extract an Emotet payload from a So many attacks start with a simple booby-trapped document that runs twitch.tv/mattifestation/ Analysis Notes: gist.github.com/mattifestation/15bd6bbb26becb2e49461400e7bd8c92. Fireeye made a white paper on cmd.exe command obfuscation (DOSfuscation). We If you would to support the channel and I, Kite! Kite is a coding assistant that helps you code faster, on any IDE offer ... videos.didierstevens.com/2017/03/06/maldoc- A Realistic Training platform designed for SOC analysts 80+ Investigation Cases 10+ Challenges 7+ Courses